











SOC 2 for Small Businesses: Scope, Cost and Timeline
Discover what SOC 2 compliance means for small businesses, from understanding the requirements and choosing the right audit scope to managing costs, timelines and ongoing evidence collection. This practical guide breaks down how startups and scaling organizations can prepare for their first SOC 2 audit, avoid common challenges and build a manageable approach to security and compliance without the need for enterprise-sized resources.

Discover what SOC 2 compliance means for small businesses, from understanding the requirements and defining the right audit scope to managing costs, timelines, and ongoing evidence collection. This practical guide explains how startups and growing businesses can prepare for their first SOC 2 audit, avoid common challenges, and build a manageable approach to security and compliance without needing enterprise-sized resources.
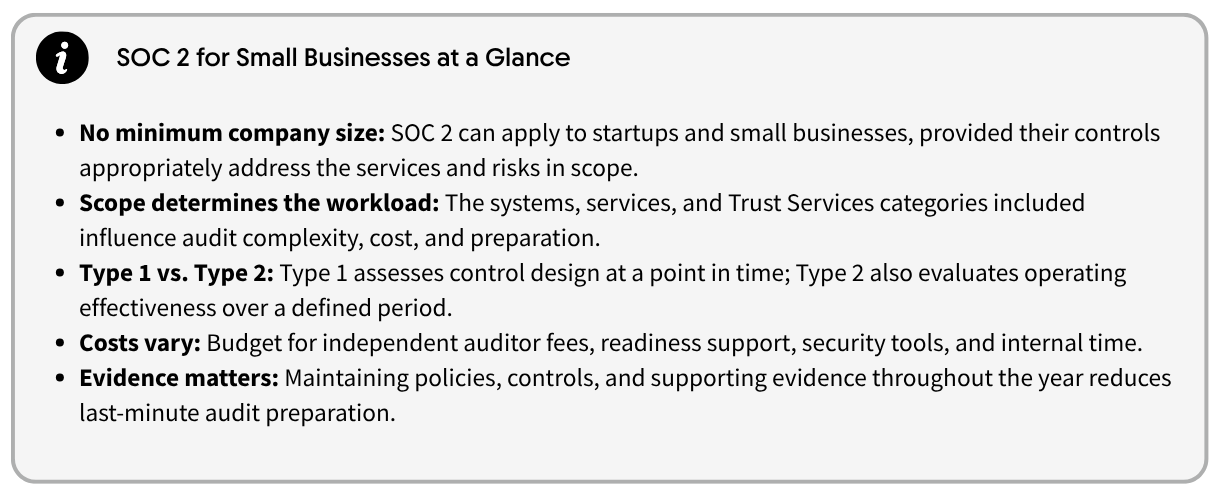
The short answer: Yes. Small businesses can achieve SOC 2 compliance without a dedicated security department or enterprise-sized budget. What matters is having appropriate controls, clear accountability, and evidence that demonstrates those controls are working.
For many small businesses, SOC 2 becomes a priority when a prospective customer asks for a report during procurement. Suddenly, what started as a security questionnaire becomes a requirement for winning a contract.
But SOC 2 doesn't need to become an overwhelming compliance project. With the right scope, preparation, and ongoing processes, smaller organizations can build a manageable program that supports customer confidence and long-term growth.
Can a Small Business Really Achieve SOC 2 Compliance?
Yes. SOC 2 is not reserved for large enterprises.
Developed by the American Institute of Certified Public Accountants (AICPA), SOC 2 provides an independent examination of controls relevant to security, availability, processing integrity, confidentiality, and privacy.
Unlike ISO 27001, SOC 2 is not a certification. An independent licensed CPA firm examines your systems and controls and issues an attestation report.
For a small SaaS business, this might involve demonstrating how customer data is protected, access is managed, incidents are handled, and security responsibilities are assigned.
The same underlying Trust Services Criteria apply regardless of company size, but the controls and evidence should reflect your organization's actual operations.
The biggest challenge for small businesses is often capacity. The person responsible for SOC 2 may also be managing IT, operations, or product development.
That's why establishing clear ownership and a realistic scope from the beginning matters.
Keeping Your SOC 2 Scope Manageable
One of the biggest factors influencing the cost and complexity of SOC 2 compliance for small businesses is scope.
Your SOC 2 report describes a defined system and the controls relevant to the services provided to customers. It doesn't necessarily need to cover every product, department, or business activity.
For a small SaaS company, the scope might include its production platform, supporting cloud infrastructure, employees with access to customer data, and relevant third-party providers.
You also need to determine which Trust Services categories apply.
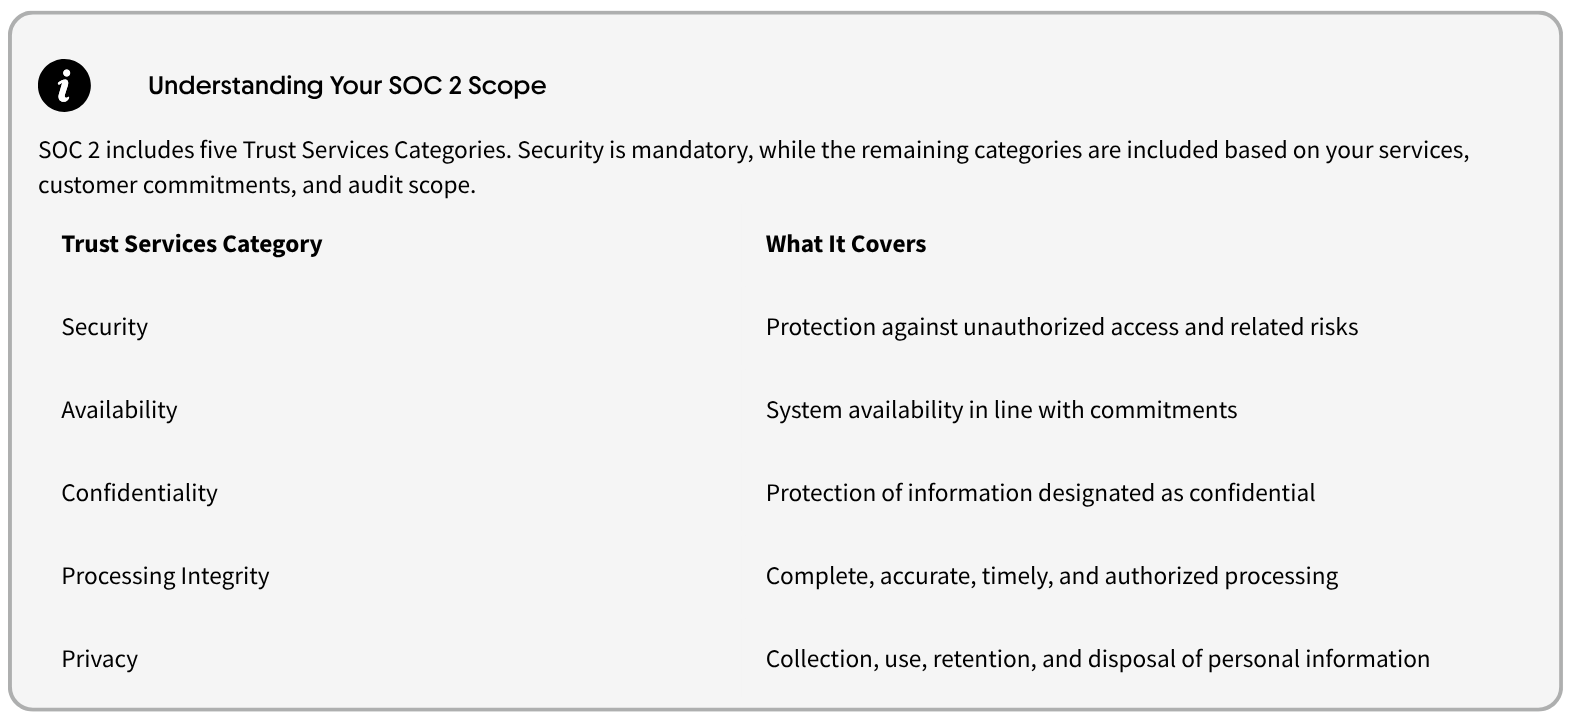
Security is required for every SOC 2 examination. The other categories are included where relevant to your services, commitments, and customer requirements.
For small businesses, the goal is to define a defensible scope that reflects what customers rely on, without introducing unnecessary complexity.
What Does SOC 2 Cost for a Small Business?
There is no fixed SOC 2 audit cost. Fees depend on your report type, system complexity, audit scope, auditor, and existing security maturity.
For planning purposes, smaller organizations may encounter audit fees starting in the high thousands of US dollars, while more complex engagements can cost substantially more. Published planning ranges from specialist CPA firms commonly extend into the tens of thousands.
However, the independent audit is only one part of the overall cost.
Budget for four areas:
- Auditor fees: The cost of an independent CPA firm examining your controls and issuing the SOC 2 report.
- Readiness support: Compliance software, consulting, or internal resources used to prepare for the examination.
- Security tools: Any additional tools or testing needed to implement and demonstrate effective controls.
- Internal time: The effort involved in policies, risk assessments, evidence collection, and audit coordination.
For small businesses, internal capacity can be as significant as the auditor's invoice.
A compliance platform can help reduce administrative effort by centralizing controls, assigning responsibilities, and keeping evidence connected to relevant requirements.
The important distinction is that SOC 2 software supports audit readiness; it does not replace the independent CPA examination.
How Long Does SOC 2 Take for a Small Business?
The timeline depends on your existing controls, the report type, and how quickly you can address identified gaps.
Some small businesses can complete initial readiness work in a few months. Others need longer to establish policies, implement controls, and build reliable evidence processes.
The biggest distinction is between SOC 2 Type 1 and Type 2.
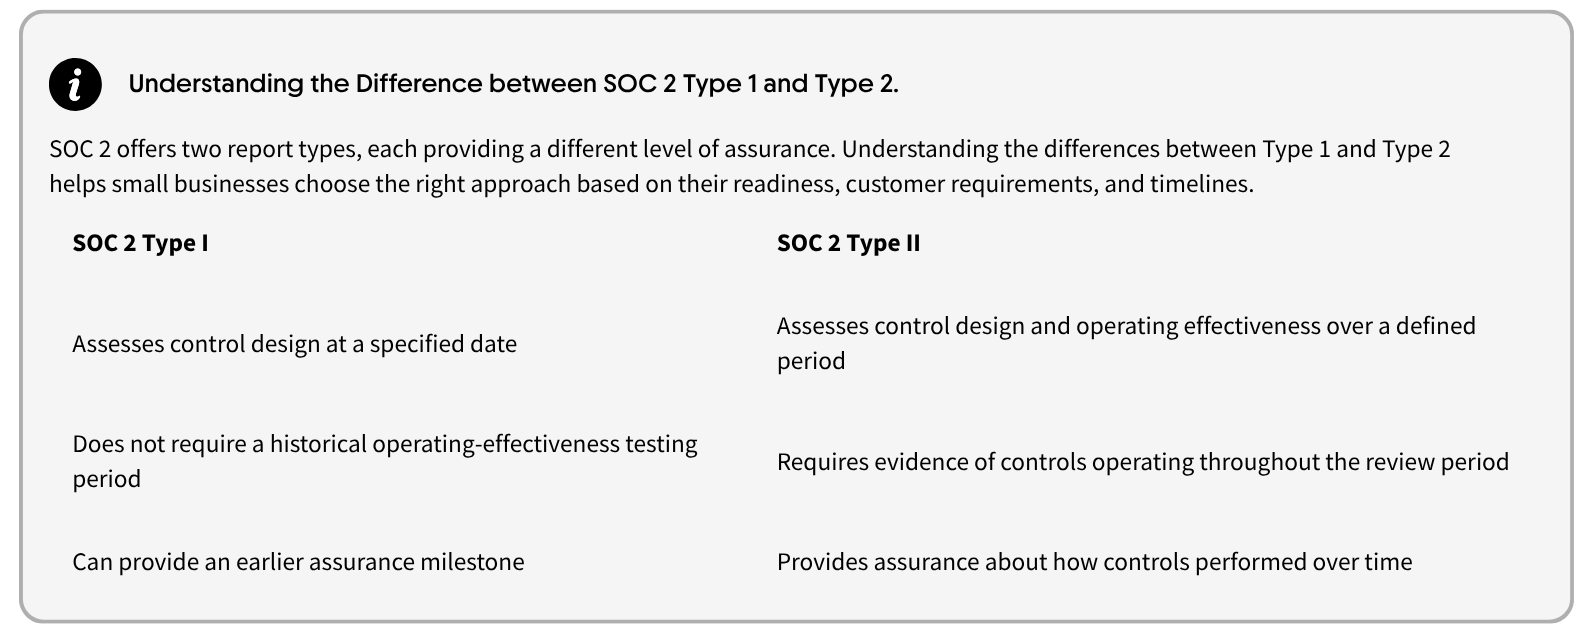
A first-time Type 2 examination commonly uses a three-to-twelve-month review period, depending on the engagement and auditor requirements.
If a customer has requested SOC 2, confirm whether they expect Type 1 or Type 2 before committing to a timeline.
A Type 1 report may be a useful first milestone, but it won't automatically satisfy a customer requiring Type 2.
Four SOC 2 Mistakes Small Businesses Can Make
1. Choosing an Unnecessarily Broad Scope
Including every system, department, and Trust Services category can increase audit complexity without delivering additional value.
Start with the services customers rely on and the controls necessary to support them. Agree on the scope with your auditor early.
2. Treating SOC 2 as an IT-Only Project
SOC 2 involves more than technical security controls.
Employee onboarding, access approvals, supplier management, risk assessments, and incident response all require involvement from across the business.
Without clear ownership, important activities can fall between teams.
3. Relying on Policies That Don't Reflect Reality
Downloading a policy template doesn't demonstrate that a control is operating.
Auditors need evidence that documented processes reflect what actually happens, from access reviews to incident handling and employee awareness.
Templates are a starting point, not a substitute for implementation.
4. Relying on Policies That Don't Reflect Reality
One of the most common challenges is keeping evidence scattered across emails, spreadsheets, and shared folders.
For Type 2 examinations, auditors assess how controls operated throughout the review period.
Establishing a structured evidence process from the beginning helps reduce retrospective searching and makes gaps easier to identify.
SOC 2 or ISO 27001: Which Is Better for a Small Business?
For small businesses evaluating security assurance requirements, SOC 2 and ISO 27001 are often considered together.
Both help organizations demonstrate that security risks are being managed, but they take different approaches.
SOC 2 is an independent attestation report examining controls relevant to the selected Trust Services categories. It's commonly requested by US enterprise customers, particularly from SaaS and technology service providers.
ISO 27001 is an international certification standard for establishing and maintaining an Information Security Management System (ISMS).
The right approach depends on customer requirements, target markets, and your existing compliance program.
If your largest prospective customer specifically requires SOC 2 Type 2, ISO 27001 certification may not satisfy that requirement.
However, organizations managing both can reuse relevant policies, risk assessments, controls, and evidence rather than maintaining entirely separate programs.
For growing businesses, that overlap can make a significant difference to ongoing compliance effort.
Our ISO 27001 vs SOC 2 Interactive Tool compares which approach is better for your business based on your geography, customers and industry - try it for yourself.
Hicomply's Take
Small businesses don't need enterprise-sized compliance teams to prepare for SOC 2.
What they need is a realistic scope, clear accountability, and an approach to managing controls and evidence that doesn't consume time better spent growing the business.
The mistake is treating SOC 2 as a one-time exercise to satisfy a customer request.
By building the right foundations early, organizations can reduce repeated audit preparation, respond more confidently to security questionnaires, and support future compliance requirements without starting again.
The Smarter Path to SOC 2: On-Demand Webinar
Hicomply partnered with Drummond to explore the most valuable path for businesses looking to achieve their first SOC 2 certification.
Catch up on the live recording over your next coffee break to hear both the auditor and operational perspective.
Get SOC 2 Audit-Ready Without Building a Compliance Department
For small businesses, the biggest barrier to SOC 2 readiness isn't always implementing security controls. It's finding the time to manage policies, coordinate responsibilities, maintain evidence, and demonstrate that everything is working.
Hicomply helps organizations bring their whole compliance program together in one place.
Our whole-business ISMS platform supports policy management, risk assessments, control monitoring, evidence management, and cross-framework mapping, helping smaller teams reduce manual administration and maintain visibility into their audit readiness.
And we're more than just a platform. Every Hicomply customer benefits from unlimited support from our in-house compliance experts throughout their compliance journey.
Preparing for your first SOC 2 audit?
Explore our SOC 2 readiness resources or book a demo to see how Hicomply can help you establish a more connected, manageable approach to compliance.
Frequently Asked Questions
Can a small business get SOC 2 compliant?
Yes. There is no minimum employee count for SOC 2. Small businesses can undergo an independent SOC 2 examination by implementing appropriate controls, defining their scope, and demonstrating that their controls meet the relevant Trust Services Criteria.
How much does SOC 2 cost for a small business?
SOC 2 costs vary depending on scope, report type, auditor, and readiness. Small businesses should budget for independent CPA examination fees, preparation, security tools, and internal time. Auditor fees can range from several thousand to tens of thousands of dollars.
How long does SOC 2 take for a startup?
Initial readiness may take a few months, depending on existing controls. Type 1 assesses controls at a point in time, while Type 2 requires evidence of operating effectiveness over a defined period, often three to twelve months.
Does a small business need SOC 2 Type 1 or Type 2?
It depends on customer requirements. Type 1 assesses whether controls are suitably designed at a specified date. Type 2 additionally assesses whether those controls operated effectively over a period. Many enterprise customers prefer Type 2 because it provides assurance over time.
Is SOC 2 mandatory for small businesses?
SOC 2 is generally not a legal requirement. However, customers, procurement teams, and commercial partners may require a SOC 2 report before entering into or renewing contracts, particularly when a business handles sensitive customer information.
Ready to Take Control of Your Privacy Compliance?
See how Hicomply can accelerate your path to CAF compliance in a 15-minute demo.