












Build Essential Eight maturity without the spreadsheet scramble
Manage Essential Eight strategies, security controls and evidence in one platform.

What is the Essential Eight, and why does it matter?
The Australian Cyber Security Centre’s Essential Eight is a set of mitigation strategies designed to help organisations reduce the risk and impact of common cyber threats. Hicomply gives teams a practical way to assign owners, map controls, collect evidence and track maturity over time.

Manage control ownership, evidence and maturity reporting across essential services and public-sector environments.

Build a proportionate cyber baseline without creating a separate spreadsheet programme for every control.

Coordinate security evidence alongside privacy, risk and assurance obligations with clear ownership.

Demonstrate a mature security programme to customers, partners and procurement teams.
A clear path to Essential Eight maturity
Scope your environment, assess maturity, assign work and maintain evidence in a repeatable programme.
Identify systems in scope, assess current controls and agree a target maturity profile.
Assign remediation, manage policies and collect evidence for each mitigation strategy.
Review maturity, prepare assurance reporting and establish an ongoing control cycle.
Essential Eight management that supports real progress
Clear evidence, accountable owners and an always-current view of cyber maturity.

Structured workflow across 4 objectives and 41 outcomes turns months of evidence collection into manageable phases

IGP mapping without tick-box exercises. Document what you achieved, not just what controls you deployed

Red, Amber, Green scoring across all contributing outcomes. Know your posture before independent assessors arrive

Toggle between Baseline and Enhanced profiles based on threat model and essential function criticality

Continuous monitoring keeps outcomes current. Essential services don't get downtime for assessment prep

Export-ready evidence packages formatted for NCSC-assured assessors. Format and structure already handled
An all-in-one Essential Eight toolkit
Manage mitigation strategies, risk, policies, evidence and improvement work in one platform.
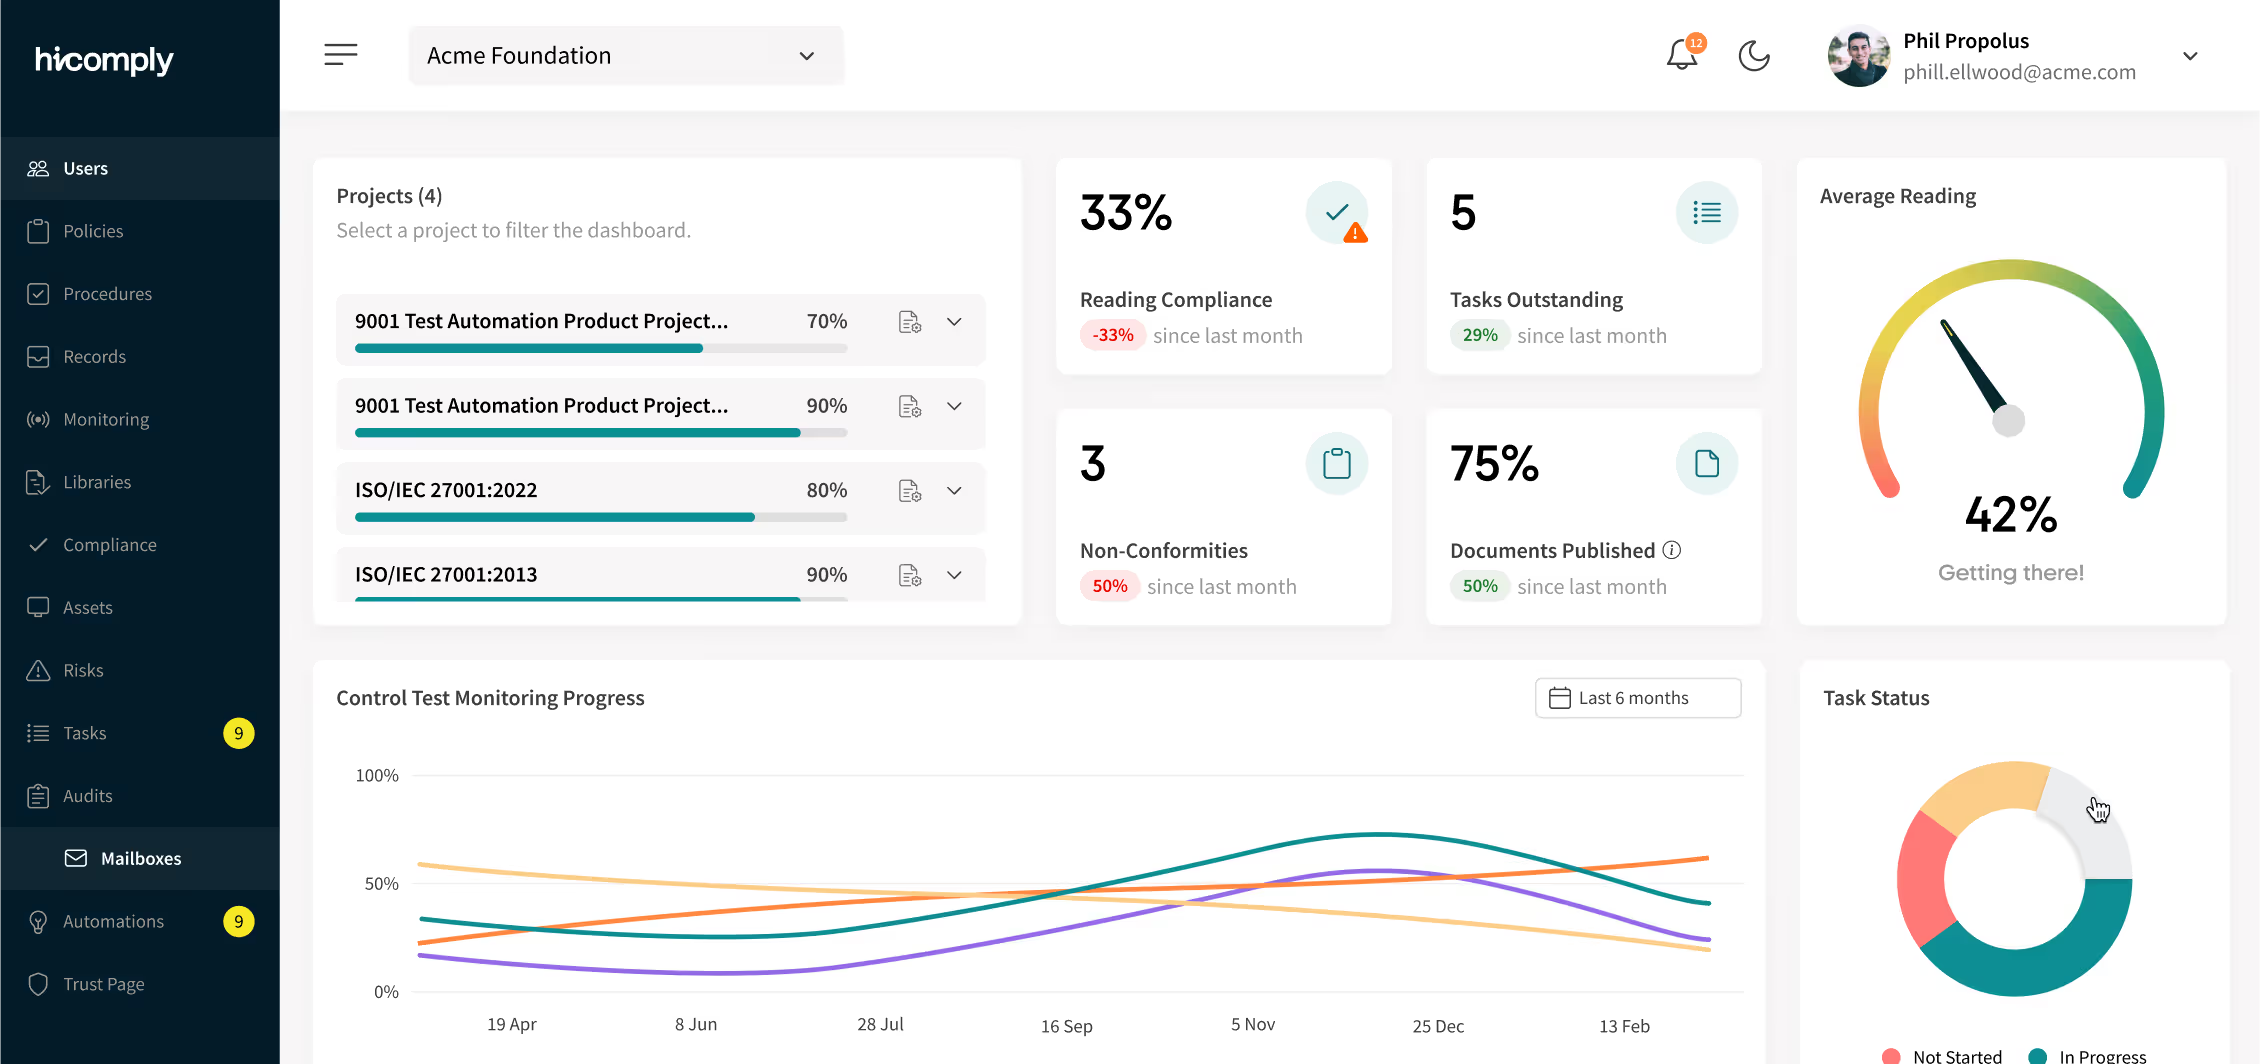
Real-time maturity tracking across all 41 contributing outcomes with Red/Amber/Green status visibility and evidence gaps highlighted

Live progress tracking across 4 CAF objectives with ownership assignments, IGP completion rates, and target deadlines

Automated linking of your technical controls, policies, and processes to Indicators of Good Practice requirements

Switch between Baseline and Enhanced profiles with automatic outcome adjustments, compensating controls documentation, and threat model alignment

CAF 4.0 adversary TTPs integrated into your risk assessments with recommended control mappings to contributing outcomes

One-click evidence packages pre-formatted for NCSC-assured assessors, organised by objective, principle, and outcome

Chosen by CNI operators and essential service providers
From first CAF assessment to continuous resilience, organisations use Hicomply to maintain cyber maturity without expanding security teams.
Hicomply has completely transformed the way that we manage our ISO27001 certification. We purchased Hicomply a few months before our re-certification was due. Zoe worked with us to set up everything up and show us how to use the platform most efficiently. She has been an amazing support to myself and my colleague as we navigated through this process.

"Implementing Hicomply has streamlined our compliance processes, making it more efficient to manage and maintain our ISO certifications. The platform's intuitive design and comprehensive features have been instrumental in enhancing our operational excellence."

“The things that we've seen this product and service deliver has far exceeded what we originally thought we would get from it."
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
From start to finish, the service and engagement from Hicomply has been fantastic… Whenever we had any questions, the team were always on hand to offer advice.
Hicomply has reduced our compliance preparation time by over 50%, ensuring we’re always audit-ready. It’s a game-changer for maintaining trust with clients.
I have found Hicomply to be incredibly useful as a platform for a new company… it has taken the stress out of our hands.
Organization at its finest. A great sorting system—I can easily find new articles that I need to review with a click.
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direct reports have completed.
Possibly the most helpful feature about Hicomply is the UI itself—user-friendly and easy to use without over-complicating things.
Hicomply has helped our business automate and simplify our compliance… No more checking shared drives or the intranet.
Great app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
“The real benefit of Hicomply, as far as I’m concerned, is twofold: the software and the personnel. It’s an all-encompassing tool that consolidated everything and enabled us to deliver on our commitments with confidence.”

Hicomply is particularly user-friendly for someone unfamiliar with this type of software… It’s making us more organised.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direGreat app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.ct reports have completed.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
Ready to prove outcome-based resilience?
See how critical infrastructure teams go from evidence chaos to assurance confidence.
CAF hub highlights
The essential guides, checklists and templates that actually help.
Got questions? Start here
Planning CAF assessment? These will help.For anything else, just ask.
What is the NCSC Cyber Assessment Framework?
CAF is the UK's flagship cybersecurity assessment framework developed by the National Cyber Security Centre. It provides an outcome-focused, systematic approach for assessing how effectively organisations manage cyber risks to essential functions. Unlike prescriptive control frameworks, CAF focuses on what you achieve rather than dictating how you achieve it.
Who should consider the Essential Eight?
The ACSC recommends the Essential Eight as a cyber security baseline for organisations. It is relevant to small and medium businesses, large organisations, critical infrastructure and government; each organisation should set its target maturity level according to its own risk profile and requirements.
What does the Essential Eight cover?
The Essential Eight covers application control, application patching, Microsoft Office macro settings, user application hardening, restriction of administrative privileges, operating-system patching, multi-factor authentication and regular backups.
How is Essential Eight maturity assessed?
The ACSC Essential Eight Maturity Model provides advice on implementing the eight mitigation strategies. Organisations can use it to assess current practices, set a risk-informed target maturity level and prioritise improvement work.
What's the difference between Baseline and Enhanced profiles?
Baseline Profile: Minimum standard for most critical systems. Modeled on untargeted attacks by unskilled adversaries.
Enhanced Profile: Higher standard for CNI and high-value targets. Modeled on attacks by moderately skilled or expert adversaries (nation-state actors, APTs).
Profile assignment depends on risk to life, sensitive data handling, national security functions, and threat landscape.
What changed in CAF 4.0?
Released August 2025, CAF 4.0 introduced significant enhancements:
- Enhanced threat understanding (A2.b): Proactive threat intelligence integration into risk decisions
- Secure software development lifecycle (A4.b): Secure-by-design principles and SBOM requirements
- Advanced monitoring and threat hunting (C1 & C2): Behavioral baseline analysis and repeatable threat hunting
- AI and automated decision-making: AI-specific risk assessments integrated across outcomes
- Elevated threat model: Focus on capable, well-resourced adversaries rather than just common threats
How does CAF differ from ISO 27001?
CAF: Outcome-focused NCSC framework for essential services and CNI. Assesses what you achieve against capable adversaries.
ISO 27001: International ISMS standard with prescriptive controls. Certifiable, focuses on information security management system.
Many organisations implement both—ISO 27001 for international recognition, CAF for UK essential services compliance. Evidence overlap is significant.
What's the relationship between CAF and NHS DSPT?
NHS DSPT aligned with CAF in September 2024. CAF-aligned DSPT includes:
- 47 contributing outcomes (41 core CAF + 6 health-specific)
- Same maturity assessment (Not Achieved, Partially Achieved, Achieved)
- Independent audit requirements for Category 1 & 2 NHS organisations
DSPT is essentially CAF applied to healthcare with sector-specific additions.
How long does an Essential Eight uplift take?
There is no fixed timeframe. An Essential Eight uplift depends on current maturity, target level, technology, available resources and the remediation required. Start with a baseline assessment, assign accountable owners and prioritise changes by risk.
Do we need independent assurance?
Most sectors require independent assurance reviews from:
- NCSC Cyber Resilience Audit Scheme providers
- Competent Authority oversight
- Third-party validation of self-assessments
- Annual review cycles for CNI and OES
Category 1 & 2 NHS DSPT organisations require independent audits. OES under NIS Regulations face Competent Authority assessment.
How does Hicomply help with CAF compliance?
We automate outcome management: 41 contributing outcomes tracked with IGP evidence mapping, maturity scoring across objectives, profile management (Baseline/Enhanced switching), threat intelligence integration for CAF 4.0, and assurance-ready documentation exports. You focus on achieving resilience outcomes; we handle evidence coordination and maturity tracking. When NCSC-assured assessors arrive, documentation exports in their expected format.
Can we use Hicomply for both CAF and ISO 27001?
Yes. CAF and ISO 27001 have significant control overlap. Hicomply's unified evidence management means documentation collected for CAF supports ISO 27001 requirements and vice versa. One evidence collection process, multiple framework outputs. That satisfying moment when one control achieves outcomes in both frameworks.