












Manage privacy obligations without the spreadsheet scramble
Build a practical privacy-management system for Australian Privacy Principles, customer assurance and global obligations.

What is privacy management, and why does it matter?
Privacy management helps teams understand how personal information is collected, used, disclosed and protected. Hicomply provides a structured way to organise policies, risks, responsibilities, evidence and improvement work for Australian organisations and their global customers.


Give customers and partners confidence that privacy is managed through accountable, documented processes.

Keep policies, privacy requests, information-handling records and assurance evidence in one place.

Respond consistently to security and privacy questionnaires with current, well-organised evidence.
A clear path to privacy readiness
Map information handling, set responsibilities, improve controls and maintain evidence through a repeatable cycle.
Scope information handling, establish owners and complete a privacy baseline assessment.
Maintain policies, collection notices, consent controls where required, training and evidence.
Review privacy risks, request workflows and evidence for management and customer assurance.
Privacy management that works for Australian teams
Less administrative overhead, clearer accountability and a stronger record of how personal information is handled.

A guided programme turns privacy obligations into manageable, accountable work.

Organise approvals, evidence and improvement actions without starting from a blank spreadsheet.

Prepare clear privacy information for customer, procurement and partner reviews.

Build a foundation that supports Australian Privacy Principles and relevant international privacy obligations.

Keep privacy risks, evidence and actions visible between formal reviews.

Provide a clear record for internal reviews, customers and advisers when it is needed.
All-in-one privacy management toolkit
Manage policies, information handling, privacy requests, risks and evidence in one workflow.
Maintain an inventory of personal information, owners, systems and retention decisions.

Manage approved policies, notices and supporting procedures with clear owners and review dates.

Coordinate access, correction, complaint and other privacy requests with accountable workflows.

Maintain a clear record of permissions and communication preferences where consent is required.

Connect relevant people, systems and workflows to reduce manual evidence gathering.

Prepare current privacy information for faster customer and vendor-assessment responses.

Chosen by privacy and compliance leaders
From first implementation to renewal, customers use Hicomply to stay ready without the scramble.
Hicomply has completely transformed the way that we manage our ISO27001 certification. We purchased Hicomply a few months before our re-certification was due. Zoe worked with us to set up everything up and show us how to use the platform most efficiently. She has been an amazing support to myself and my colleague as we navigated through this process.

"Implementing Hicomply has streamlined our compliance processes, making it more efficient to manage and maintain our ISO certifications. The platform's intuitive design and comprehensive features have been instrumental in enhancing our operational excellence."

“The things that we've seen this product and service deliver has far exceeded what we originally thought we would get from it."
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
From start to finish, the service and engagement from Hicomply has been fantastic… Whenever we had any questions, the team were always on hand to offer advice.
Hicomply has reduced our compliance preparation time by over 50%, ensuring we’re always audit-ready. It’s a game-changer for maintaining trust with clients.
I have found Hicomply to be incredibly useful as a platform for a new company… it has taken the stress out of our hands.
Organization at its finest. A great sorting system—I can easily find new articles that I need to review with a click.
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direct reports have completed.
Possibly the most helpful feature about Hicomply is the UI itself—user-friendly and easy to use without over-complicating things.
Hicomply has helped our business automate and simplify our compliance… No more checking shared drives or the intranet.
Great app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
“The real benefit of Hicomply, as far as I’m concerned, is twofold: the software and the personnel. It’s an all-encompassing tool that consolidated everything and enabled us to deliver on our commitments with confidence.”

Hicomply is particularly user-friendly for someone unfamiliar with this type of software… It’s making us more organised.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direGreat app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.ct reports have completed.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
Ready to nail GDPR compliance?
See how teams go from spreadsheet chaos to audit confidence.
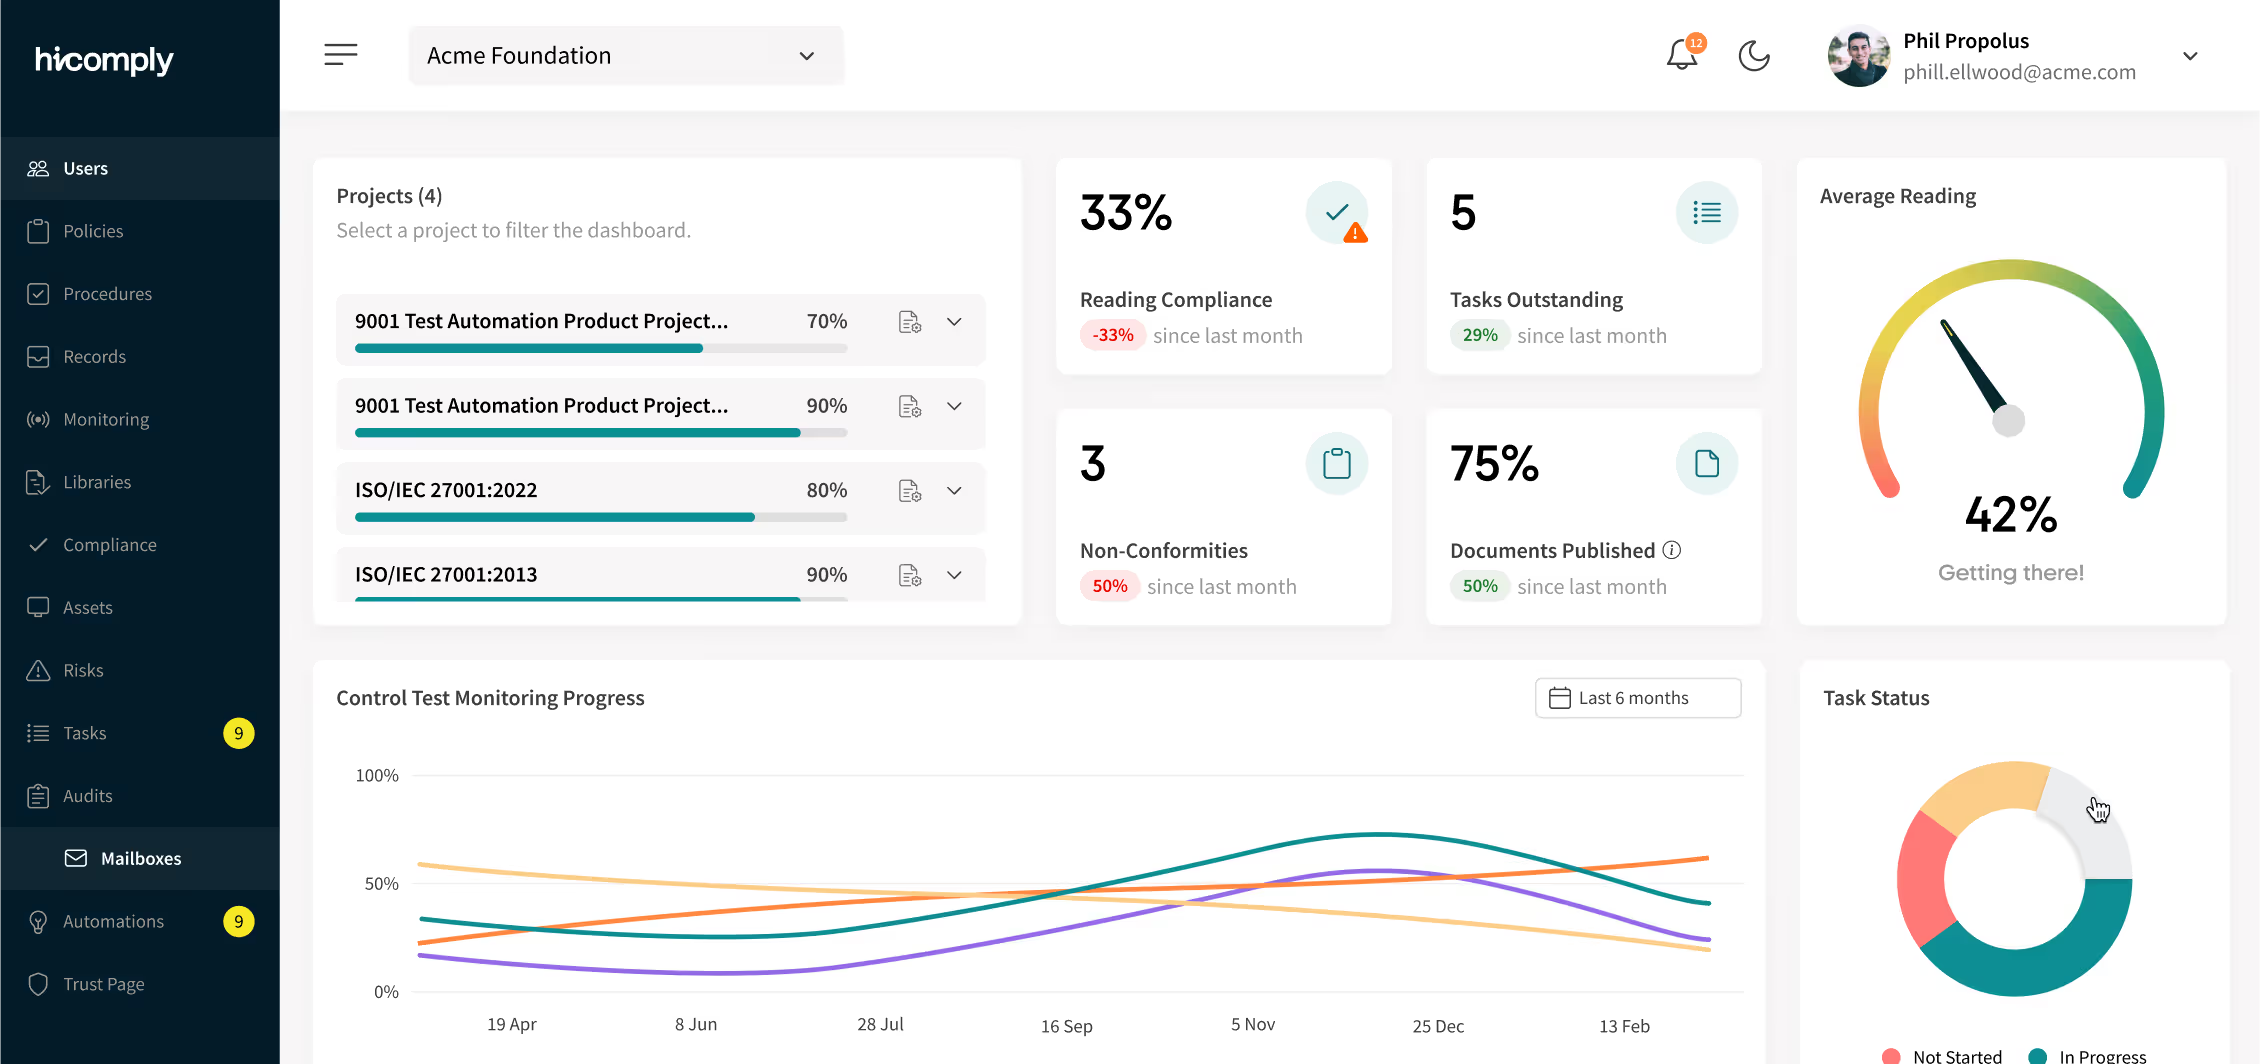
GDPR hub highlights
The must-read guides, checklists and samples in one place.
Got questions? Start here
Planning your privacy program? These will help. For anything else, just ask.
What is GDPR?
The General Data Protection Regulation (GDPR) is the EU's comprehensive privacy law that governs how organisations handle personal data. In effect since May 2018, it imposes strict requirements on data collection, storage, and security. GDPR applies to any organisation worldwide that processes data about people in the EU—making it a global privacy benchmark. Violations can result in fines up to €20 million or 4% of global annual turnover.
Does GDPR apply to my business?
If you offer goods or services to people in the EU, or monitor their behaviour (e.g., web analytics), GDPR applies—regardless of where your business is based. A US startup selling to European customers must comply. So must a UK firm post-Brexit (via UK GDPR).
What are the main GDPR requirements?
GDPR requires organisations to:
- Have a lawful basis for processing personal data (consent, contract, legitimate interest, etc.)
- Maintain records of processing activities
- Implement appropriate technical and organisational security measures
- Honour data subject rights (access, deletion, rectification, portability)
- Report data breaches within 72 hours
- Appoint a Data Protection Officer (in certain cases)
- Conduct Data Protection Impact Assessments for high-risk processing
How does GDPR differ from the UK Data Use and Access Act 2025?
The UK's Data (Use and Access) Act 2025 (DUAA) streamlines certain UK GDPR obligations while maintaining core protections. Key changes include:
- Recognised legitimate interests that no longer require balancing tests
- Relaxed cookie consent for analytics and functionality cookies
- "Reasonable and proportionate" limits on Subject Access Requests
- Broader consent for scientific research
- Mandatory privacy-by-design for services likely used by children
These changes lighten administrative burden in the UK while keeping privacy protections strong.
What are data subject rights under GDPR?
Individuals have the right to:
- Access their personal data
- Rectification of inaccurate data
- Erasure (right to be forgotten)
- Restriction of processing
- Data portability (receive data in machine-readable format)
- Object to processing (especially for direct marketing)
- Not be subject to automated decision-making without human review
Organisations must respond to these requests within one month (extendable by two months if complex).
How do I prepare for a GDPR audit?
Key steps include:
- Maintain an up-to-date data inventory (records of processing activities)
- Document lawful bases for all processing
- Keep consent records where applicable
- Ensure privacy policies are current and transparent
- Complete Data Protection Impact Assessments for high-risk activities
- Maintain evidence of security measures (encryption, access controls, breach procedures)
- Train staff and document awareness programs
- Review and update third-party processor agreements
Using a platform like Hicomply keeps this evidence organised and audit-ready at any time.
What are the fines for GDPR non-compliance?
GDPR operates on a tiered penalty system:
- Tier 1: Up to €10 million or 2% of global annual turnover for violations like inadequate record-keeping or breach notification failures
- Tier 2: Up to €20 million or 4% of global annual turnover for serious infringements like violating core processing principles or data subject rights
Beyond fines, regulators can issue warnings, reprimands, or processing bans. Reputational damage and loss of customer trust are equally costly consequences.
Why automate GDPR compliance?
Traditional GDPR compliance can take 6–12 months of manual documentation, spreadsheet tracking, and constant monitoring. With Hicomply, most of the work is automated—from data mapping to consent tracking to DSAR workflows. Our GDPR automation software fast-tracks compliance, reduces manual effort by up to 90%, and ensures you're always audit-ready.
Book a free demo to see it in action.
How does Hicomply support GDPR compliance?
Hicomply provides:
- Hicomply Privacy™ module with built-in GDPR framework
- Automated data mapping and processing record maintenance
- DSAR workflow management with deadline tracking
- Consent tracking and documentation
- Policy templates aligned to GDPR articles
- Integration with 75+ applications for automated evidence collection
- Real-time monitoring of compliance status
- Built-in framework updates when regulations change
Audit-ready evidence repository and reporting
Can small businesses implement GDPR?
Absolutely. GDPR principles scale with your size—you're not expected to have enterprise-grade everything from day one. The regulation is proportionate: smaller processing operations have lighter obligations. Our automation makes GDPR accessible for growing teams without the traditional consulting overhead.
What third-party tools integrate with Hicomply for GDPR?
Hicomply integrations includes:
- HR systems (BambooHR, Workday, Gusto, Rippling, ADP Workforce Now) for employee data tracking
- Cloud storage (Google Drive, OneDrive, Dropbox, Box, SharePoint) for document evidence
- Project management (Asana, ClickUp, Jira, Linear, Basecamp) for task tracking
- Ticketing systems (Zendesk, ServiceNow, Freshdesk) for DSAR workflow management
- Identity management (Okta, Azure AD, Google Workspace) for access control evidence
- File storage & collaboration for automated evidence collection
Visit our Integrations page for the complete list.
How does GDPR compliance help with other frameworks?
GDPR's data protection principles align closely with:
- ISO 27001 (information security)
- ISO 27018 (cloud privacy)
- SOC 2 (data security and privacy trust criteria)
- NIST Privacy Framework (privacy risk management)
What you build for GDPR—policies, data inventories, security controls—serves as foundation for other frameworks. Hicomply lets you map one control to multiple standards, avoiding duplicate work.