












Build an ISO 27701 privacy management system for Australia
Extend ISO 27001 with privacy controls that help Australian organisations manage personal information, Australian Privacy Principles and global obligations in one framework.
What is ISO 27701, and why does it matter in Australia?
ISO 27701 is an international extension to ISO 27001 for privacy information management. It helps organisations create a disciplined system for identifying personal-information handling, assigning responsibilities, managing risks and maintaining evidence. For Australian organisations, it can support a practical approach to privacy governance and the Australian Privacy Principles while also helping teams respond to global customer and regulatory requirements.

Maintain a clear record of privacy obligations, decisions, evidence and improvement actions.

Extend your ISO 27001 framework with privacy controls that integrate seamlessly—one system for security and privacy.

Support APP-aware privacy management, customer assurance and global privacy readiness in one system.
Turn privacy from liability into competitive advantage. Build trust that wins deals.
A clear path to privacy-ready
Extend your ISMS, define privacy responsibilities and collect evidence through a repeatable management cycle.
PIMS scoping, privacy-role definition, information-flow mapping and baseline assessment.

Policies, privacy requests, data inventory, collection-notice and consent controls where applicable.

Privacy impact assessments, evidence review and management assurance.

ISO 27701 that supports privacy governance
Systematic privacy management, stronger assurance and a more reliable record of how personal information is handled.

Support Australian Privacy Principles and global privacy obligations through a single, documented privacy-management system.

Show customers, employees, and partners that mechanisms are in place to keep their data safe.

Track access, correction, complaint and other privacy requests with accountable workflows and evidence.

ISO 27701 extends your existing ISO 27001 framework—one integrated system for security and privacy. If you're certified in ISO 27001, you're already halfway there.
Use a single PIMS framework to organise Australian and international privacy obligations.

Continuous compliance monitoring means no last-minute panic when certification audits arrive.
All-in-One Privacy Management Toolkit
Manage PII, policies, data subject rights and evidence in one workflow. Make privacy systematic.
Define controller and processor roles (Annexes A & B), map data flows, and establish privacy management system boundaries that extend your ISO 27001 ISMS
Track what personal data you hold, where it lives, who accesses it, and retention requirements
Create and maintain privacy-by-design procedures that support ISO 27701, the Australian Privacy Principles and relevant international obligations.
Manage access, rectification, erasure, portability, and objection requests within regulatory timelines
Structured PIA workflows for high-risk processing with documented risk treatment plans
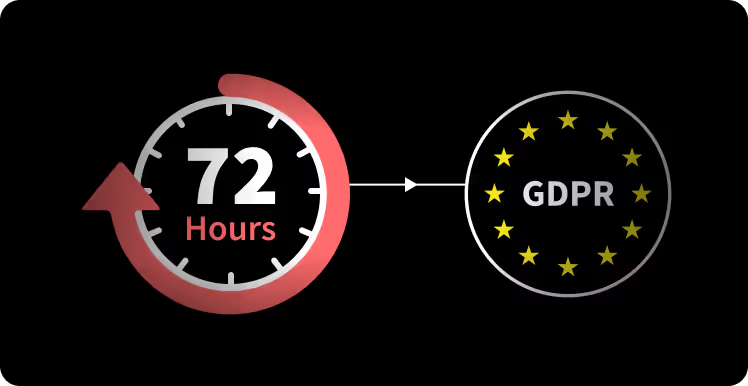
Support breach assessment and response workflows with evidence trails and decision records. Legal obligations depend on the incident and applicable law.
Why teams choose Hicomply for ISO 27701
Stories from organisations who built privacy programmes without hiring consultants.
Hicomply has completely transformed the way that we manage our ISO27001 certification. We purchased Hicomply a few months before our re-certification was due. Zoe worked with us to set up everything up and show us how to use the platform most efficiently. She has been an amazing support to myself and my colleague as we navigated through this process.

"Implementing Hicomply has streamlined our compliance processes, making it more efficient to manage and maintain our ISO certifications. The platform's intuitive design and comprehensive features have been instrumental in enhancing our operational excellence."

“The things that we've seen this product and service deliver has far exceeded what we originally thought we would get from it."
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
From start to finish, the service and engagement from Hicomply has been fantastic… Whenever we had any questions, the team were always on hand to offer advice.
Hicomply has reduced our compliance preparation time by over 50%, ensuring we’re always audit-ready. It’s a game-changer for maintaining trust with clients.
I have found Hicomply to be incredibly useful as a platform for a new company… it has taken the stress out of our hands.
Organization at its finest. A great sorting system—I can easily find new articles that I need to review with a click.
FormusPro achieved ISO 27001 certification in under six months. Less than half the typical timeline predicted by other providers.
Hicomply stands out with its intuitive interface and a truly streamlined approach to compliance management. The automation of tedious tasks has saved our team countless hours.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Hicomply delivers a refreshingly streamlined experience in compliance management… What truly sets them apart is their outstanding support.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direct reports have completed.
Possibly the most helpful feature about Hicomply is the UI itself—user-friendly and easy to use without over-complicating things.
Hicomply has helped our business automate and simplify our compliance… No more checking shared drives or the intranet.
Great app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
“The real benefit of Hicomply, as far as I’m concerned, is twofold: the software and the personnel. It’s an all-encompassing tool that consolidated everything and enabled us to deliver on our commitments with confidence.”

Hicomply is particularly user-friendly for someone unfamiliar with this type of software… It’s making us more organised.
Very interactive, not boring at all. It’s straight to the point and teaches you things in an interactive way.
Easy to use and straightforward for confirming you’ve read the necessary documents. The dashboard lets you see what your direGreat app for ISO implementation and auditing—task managing, informative dashboard, intuitive to implement.ct reports have completed.
Easy way to track compliance learning. A simple product that makes keeping up to date with policy changes simple.
Ready to turn privacy compliance into your competitive edge?
See how teams go from privacy chaos to certified confidence—without the consultant fees.
ISO 27701 hub highlights
The essential guides, checklists and templates for privacy professionals.

Got questions? Start here
Planning an audit? These will help.
For anything else, just ask.
What is ISO 27701?
ISO 27701 is the international standard for Privacy Information Management Systems (PIMS). It extends ISO 27001 with privacy-specific controls for managing personally identifiable information (PII). Think of it as the privacy layer on top of your security foundation—helping you demonstrate GDPR compliance, handle data subject rights, and manage privacy risks systematically. Related: See our ISO 27001 framework page for the security prerequisite.
Do I need ISO 27001 before ISO 27701?
Yes. ISO 27701 cannot be implemented standalone—it's an extension of ISO 27001 and ISO 27002. You must either have existing ISO 27001 certification or implement both standards simultaneously. The good news: if you're already ISO 27001 certified, you've done much of the groundwork. ISO 27701 adds privacy-specific controls (Annexes A & B) on top.
How does ISO 27701 help with GDPR compliance?
ISO 27701 provides structured processes for key GDPR requirements: Article 5 principles (accuracy, minimisation, retention), Article 12-13 transparency, Article 15-22 data subject rights, Article 33-34 breach notification, and Article 35 privacy impact assessments. Annex D provides detailed mapping between ISO 27701 controls and GDPR articles—demonstrating compliance systematically. Plus: It supports UK GDPR, CCPA, LGPD, and POPIA within one framework.
What's the difference between PII controller and processor?
PII controllers determine why and how personal data is processed—if you collect the data, you're the controller. PII processors handle data on behalf of controllers—if someone else collects it and you process it for them, you're the processor. ISO 27701 has different requirements for each role (Annex A for controllers, Annex B for processors). Many organisations operate in both roles depending on their activities.
How long does ISO 27701 implementation take?
Traditional certification? 6-12 months if you're starting from scratch with ISO 27001. If you're already ISO 27001 certified, extending to ISO 27701 typically takes 3-6 months. With Hicomply's automation, most customers are audit-ready in 8-12 weeks by automating policy generation, PII mapping, DSAR workflows, and evidence collection.
What are data subject rights under ISO 27701?
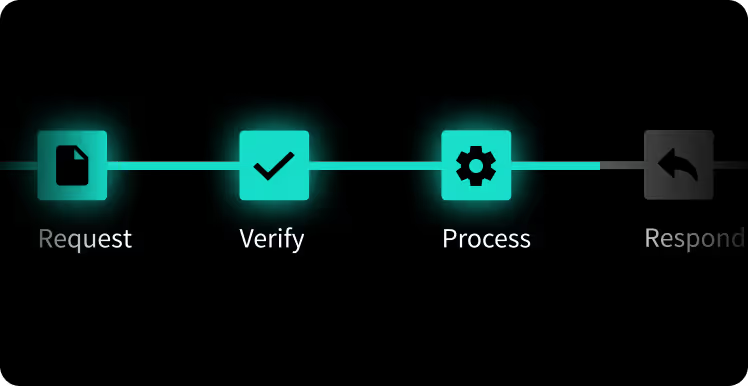
GDPR grants individuals rights over their personal data: access, rectification, erasure (right to be forgotten), portability, restriction, and objection. ISO 27701 requires documented processes to handle these requests within regulatory timelines (one month for GDPR). Hicomply provides workflows for receiving, verifying, processing, and responding to DSARs without manual scrambling.
How much does ISO 27701 certification cost?
Costs vary based on organisation size and whether you're already ISO 27001 certified. If extending existing ISO 27001: certification body fees typically £3,000-£10,000 for SMEs; larger organisations £10,000-£25,000+. Annual surveillance audits £1,500-£5,000. Compare this to GDPR fines (up to €20 million or 4% of turnover) and the competitive advantage of demonstrating privacy compliance.
How does ISO 27701 support multiple privacy regulations?
While often associated with GDPR, ISO 27701 is internationally applicable. It supports compliance with: EU GDPR, UK GDPR, California CCPA/CPRA, Brazil LGPD, South Africa POPIA, Australia Privacy Principles, and other global privacy regulations. The standard provides a universal framework that can be adapted to different regulatory requirements—one PIMS, multiple compliance demonstrations.
How does Hicomply make ISO 27701 easier?
We automate the complex bits—PII mapping, DSAR workflows, policy generation, compliance tracking, breach documentation. Your team handles privacy decisions and assessments, not administrative burden. It integrates seamlessly with your existing ISO 27001 framework in Hicomply, so you're managing security and privacy in one system. Privacy management that doesn't require a law degree. Also supports: GDPR compliance | UK GDPR | CCPA | LGPD