
















Key takeaways
• MI5 now devotes more resource to countering state threats than it did during the Cold War, and its state threats caseload has quadrupled in a decade (MI5 annual threat update, 13 October 2026).
• Hostile states are targeting businesses, supply chains and infrastructure, not just government.
• MI5 has made Protect, its work on national resilience, a third core mission alongside counter-terrorism and state threats.
• Organisations in critical infrastructure, defence supply chains and tech should implement NPSA and NCSC guidance now: "the day before, not the morning after."
What did MI5 say in its 2026 threat update?
On 13 October 2026, Sir Ken McCallum, Director General of MI5, delivered his annual threat update at Thames House.
The headline is stark.
MI5 is now devoting more resource to countering state threats than it did during the Cold War. Its state threats caseload has quadrupled in a decade, and counter-terrorism and state threats are now roughly equal in scale.
It would be easy to file that under spies and geopolitics. That would miss the point. The most striking thing about this year's speech was who it was addressed to.
Why is national security now a business issue?
Because that is where the attacks are landing.
McCallum was explicit: much of the time, those who mean the UK harm aren't attacking things the government owns or controls. They are going after people, businesses and communities.
He named the weak points. Financial systems, energy grids, supply chains and manufacturing - designed for maximum efficiency in simpler times, and now open to disruption and coercion.
He cited a destructive cyber attack on a UK energy generator, arson against European defence companies, and an individual charged last month for allegedly preparing to sabotage a drone factory in Swindon.
MI5's response is to elevate its protective work, which it calls Protect, to a third core mission alongside counter-terrorism and state threats. That is a significant signal. The UK's security service is saying, in public, that national resilience cannot be delivered by government alone.
What did MI5 tell businesses to do?
Prepare now, using official guidance. Critical infrastructure operators and defence suppliers, large or small, should follow NPSA and NCSC guidance on counter-sabotage, hostile reconnaissance and drones.
Researchers should use Trusted Research advice to protect their work. Tech start-ups were told to expect to be spied on by foreign actors, and to sort their cybersecurity.
On timing, McCallum was clear: implement the guidance "the day before, not the morning after."
How is AI changing the threat?
McCallum also announced the AI Threat Assessment Centre, housed in MI5 and drawing on expertise from the AI Security Institute, the National Crime Agency and the NCSC.
His assessment is that AI is already supercharging the contest between cyber attackers and defenders. For most organisations, that means attacks are getting cheaper to launch and harder to spot.
Defenders need to use it too, but with care.
AI can take the legwork out of security and compliance. The judgement calls should stay with the people accountable for them.
Why does resilience need to cover the whole business?
Here is the point we would draw out: State-backed threats don't stay inside your cloud console.
The tactics McCallum described — fake headhunter profiles used to target staff, hostile reconnaissance, insider risk, supplier pressure, sabotage — cut across people, premises, suppliers and process as much as technology.
ISO 27001 has always recognised this.
Around 63% of its controls are organisational, people or physical rather than technical. Cloud configuration still matters: environments change constantly, and one misconfiguration can leave a door open.
But a security programme that only watches infrastructure leaves most of the attack surface unmanaged.
Resilience also must be continuous. A certificate earned once describes your security posture on audit day. Adversaries test you on every other day of the year.
What should UK businesses do now?
• Know which category you're in. If you operate critical national infrastructure, sit in a defence or energy supply chain, or deliver public services, NPSA and NCSC guidance applies to you, and frameworks such as the NCSC's Cyber Assessment Framework (CAF) and the NHS Data Security and Protection Toolkit set the bar. For everyone else, Cyber Essentials is the floor, not the ceiling.
• Look beyond the tech stack. Review supplier assurance, physical security, insider risk and how your people handle unsolicited approaches, including on professional networking sites.
• Make it continuous. Monitor controls year-round, keep evidence current, and test your incident response before you need it.
How Hicomply helps
McCallum said he shared his update not to provoke anxiety but to encourage preparedness. We'd say the same.
Hicomply is the audit readiness platform that pairs intelligent software with expert compliance support. We help organisations globally build and maintain an information security management system (ISMS) that supports the whole business to remain confident, accountable and continuously compliant year-round.
In the platform:
• Cloud Control Monitoring brings findings from tools such as Microsoft Defender for Cloud and AWS Security Hub into the same view as your organisational, people and physical controls. Configuration drift is flagged as it happens, and Compliance, IT and leadership work from one picture.
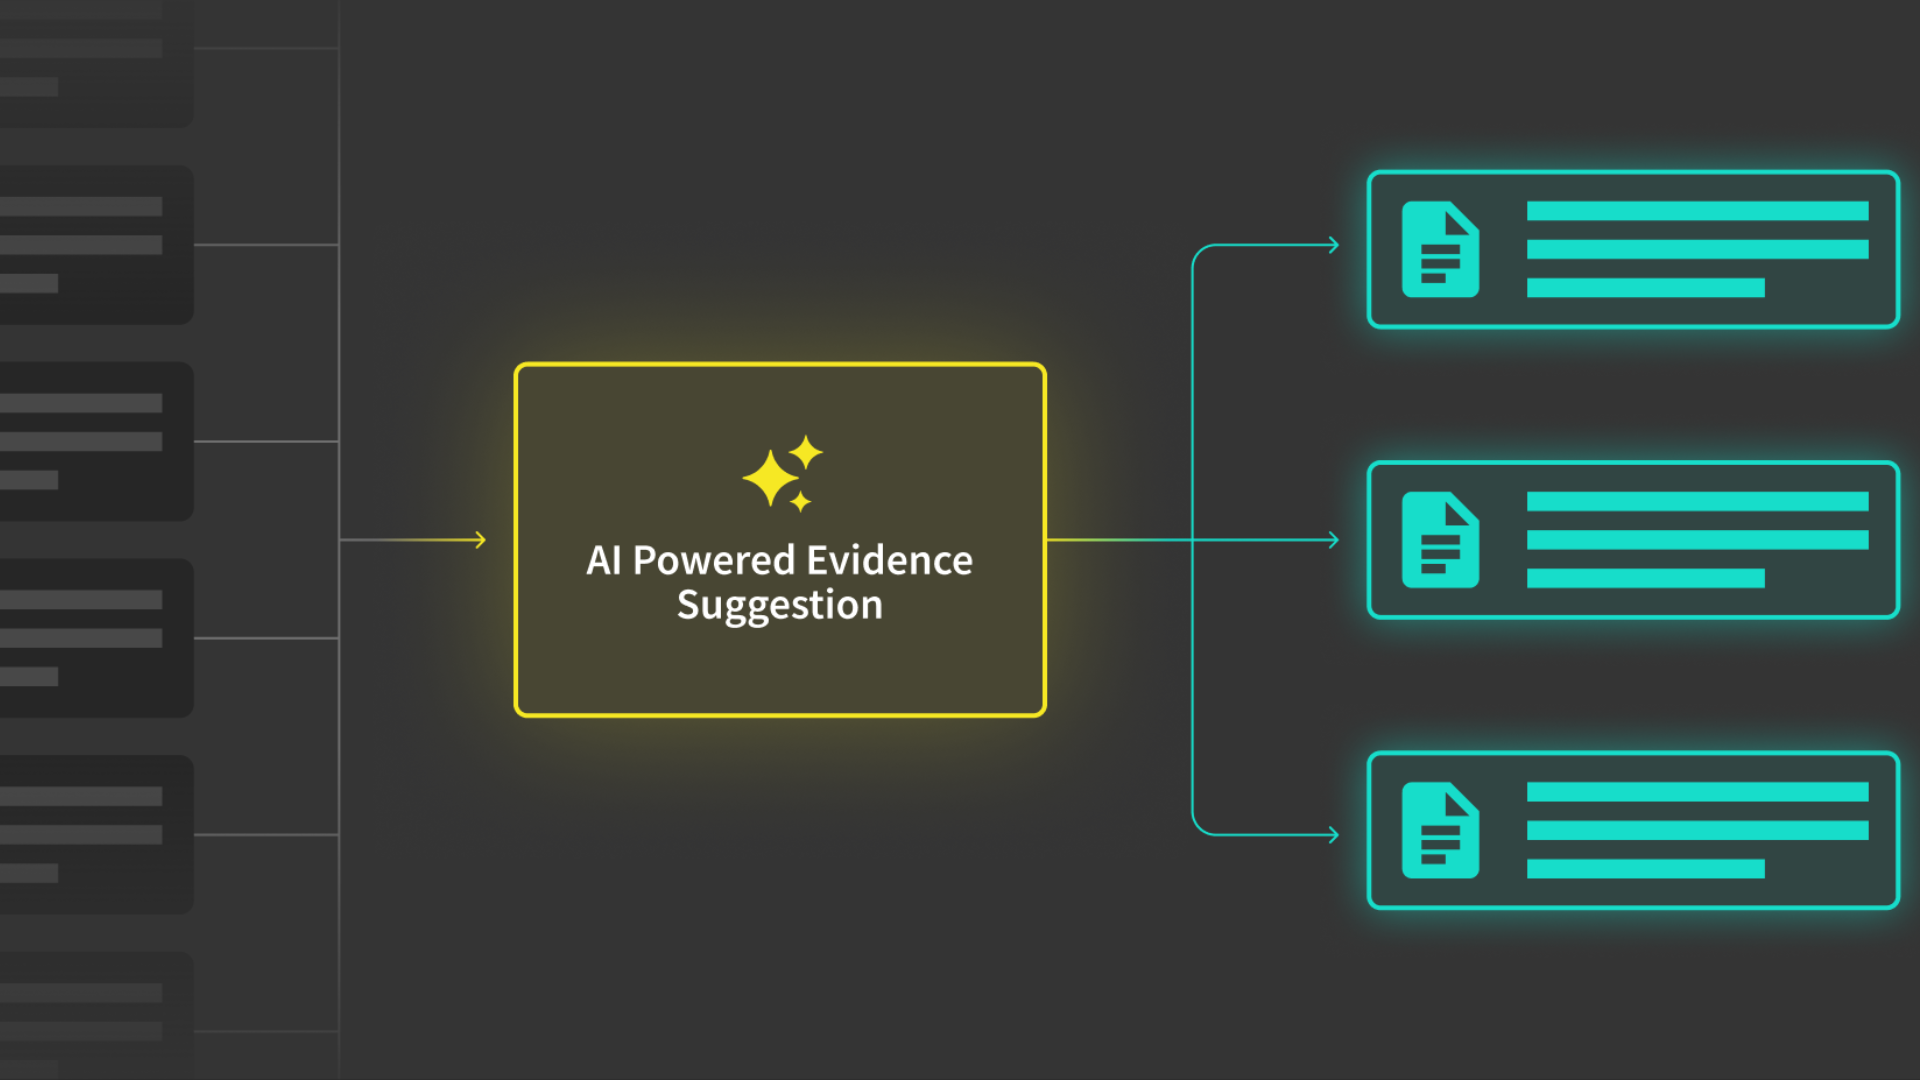
• AI-powered Evidence Discovery continuously scans your connected integrations and mailboxes and maps evidence to the right controls across every framework you manage. You review, accept or reject every suggestion, so the decisions stay with you.
• Controls Monitor then gives you a live view of audit readiness all year, not just in the run-up to an audit.
• Map your controls once across ISO 27001, Cyber Essentials, CAF, NHS DSPT and more.
From our people:
• Expert compliance support is included on every plan as standard. Our team are lead ISO implementers and offer unlimited support across the whole certification journey, from day one through to certification.
• Not only is this one of Hicomply’s services our customers love the most, this is evidence in our 100% first-time audit pass rate.
________________________________________
Sources: MI5, Director General's annual threat update, 13 October 2026; National Protective Security Authority; NCSC Cyber Assessment Framework. Also reported by BBC News.
Frequently asked questions
What did MI5 say in its 2026 annual threat update?
On 13 October 2026, MI5 Director General Sir Ken McCallum said MI5 now devotes more resource to countering state threats than it did during the Cold War, and that its state threats caseload has quadrupled over the past decade. He named Russia as the leading state aggressor and said Iran-linked operations had led to more than 50 UK arrests in the previous 12 months.
Does MI5's guidance apply to small businesses?
Yes. McCallum's advice was aimed at defence suppliers "large or small", and he told tech start-ups to expect to be targeted by foreign spies. Any organisation in a critical infrastructure or defence supply chain should follow NPSA and NCSC guidance, whatever its size.
What is the NPSA?
The National Protective Security Authority is part of MI5. It works alongside GCHQ's National Cyber Security Centre to identify vulnerabilities in UK critical infrastructure, and publishes advice on sabotage, hostile reconnaissance, insider risk, drones and cyber threats.
What is MI5's AI Threat Assessment Centre?
The AI Threat Assessment Centre (AITAC) was launched in 2026. It is housed in MI5 and draws on expertise from the AI Security Institute, the National Crime Agency and the NCSC to produce all-source assessments of how AI is being misused by hostile actors.
What is the difference between Cyber Essentials and the CAF?
Cyber Essentials is a government-backed certification covering basic technical controls that protect against the most common cyber attacks. The NCSC's Cyber Assessment Framework is broader and outcome-based, designed for organisations running essential services and critical infrastructure. It covers governance, risk management, detection and resilience as well as technical security.
How does ISO 27001 help with state-backed threats?
ISO 27001 is the international standard for an information security management system (ISMS). It covers organisational, people, physical and technological controls, so it addresses the full range of tactics MI5 describes, from insider recruitment to cyber attacks, and requires continuous improvement rather than a one-off check.