
















Why Cloud Security Is Only One Part of Compliance
Cloud security has never been more visible.
Today, organisations can continuously monitor their cloud environments, identify configuration issues, surface vulnerabilities and understand where technical controls are passing or failing.
That visibility matters. As more infrastructure, applications and data move into the cloud, understanding your cloud security posture has become an essential part of managing risk.
But it’s still only part of the wider picture.
When managing frameworks such as ISO 27001 or SOC 2, a strong cloud security posture doesn’t automatically translate into a strong compliance posture.
And this is because compliance extends beyond your infrastructure.
Cloud security gives you important signals
Cloud security platforms have transformed how organisations identify and respond to technical risk, giving teams continuous visibility into the security of their cloud environments.
Instead of relying on periodic checks, security teams can continuously assess their environments against security policies and best practices.
They can see when resources are incorrectly configured, when encryption requirements aren't being met, when access controls need attention or when changes introduce new risks.
These are important signals. And they can provide valuable evidence that technical controls are operating as expected.
But a compliance programme focuses on a broader set of questions.
It isn't only concerned with whether a technical control is configured correctly. It also needs to establish who owns that control, how the associated risk is being managed, whether the right policies and processes are in place and whether those processes are actually being followed.
And, importantly, whether the organisation can evidence all of that when required.
That context rarely exists within a cloud security platform alone.
Not every control lives in the cloud
This is where the distinction between cloud security posture and compliance posture becomes important.
Think about everything else an organisation might need to understand:
- Have employees read and accepted the latest information security policies?
- Has mandatory security training been completed?
- Are supplier risks being accessed and reviewed?
- Have outstanding internal audit actions been addressed?
- Does the risk register reflect changes across the organisation?
- Where is the evidence that demonstrates controls are operating effectively?
Of course, none of this makes cloud security monitoring less valuable. It simply demonstrates why compliance can't be viewed exclusively through a technical lens.
Frameworks such as ISO 27001 address information security across the organisation. Technology is part of that, but so are people, processes, governance, suppliers, physical security and organisational responsibilities.
Your cloud environment can therefore be secure while gaps still exist elsewhere in your compliance programme.
The challenge is connecting those different views
For many organisations, the problem isn't a lack of information. It's that the information exists in different places.
Cloud security teams may be working from specialist tools. Compliance teams may be managing controls elsewhere. Evidence sits across shared drives, inboxes, ticketing platforms and other business systems. Risks have their own owners and processes.
Each system might be doing its job.
But understanding the organisation's overall compliance posture becomes much harder when those signals remain disconnected.
For example, take a failed cloud configuration. The technical finding itself is important, but from a compliance perspective there is more to understand.
Which controls does it affect? Which frameworks does it relate to? Does the same issue affect requirements across multiple frameworks? Who needs to take action? And what does it mean for the organisation's wider compliance posture?
That's the connection organisations need to make.
From cloud findings to compliance context
The answer isn't to replace specialist cloud security tooling with compliance software. It's to connect the two.
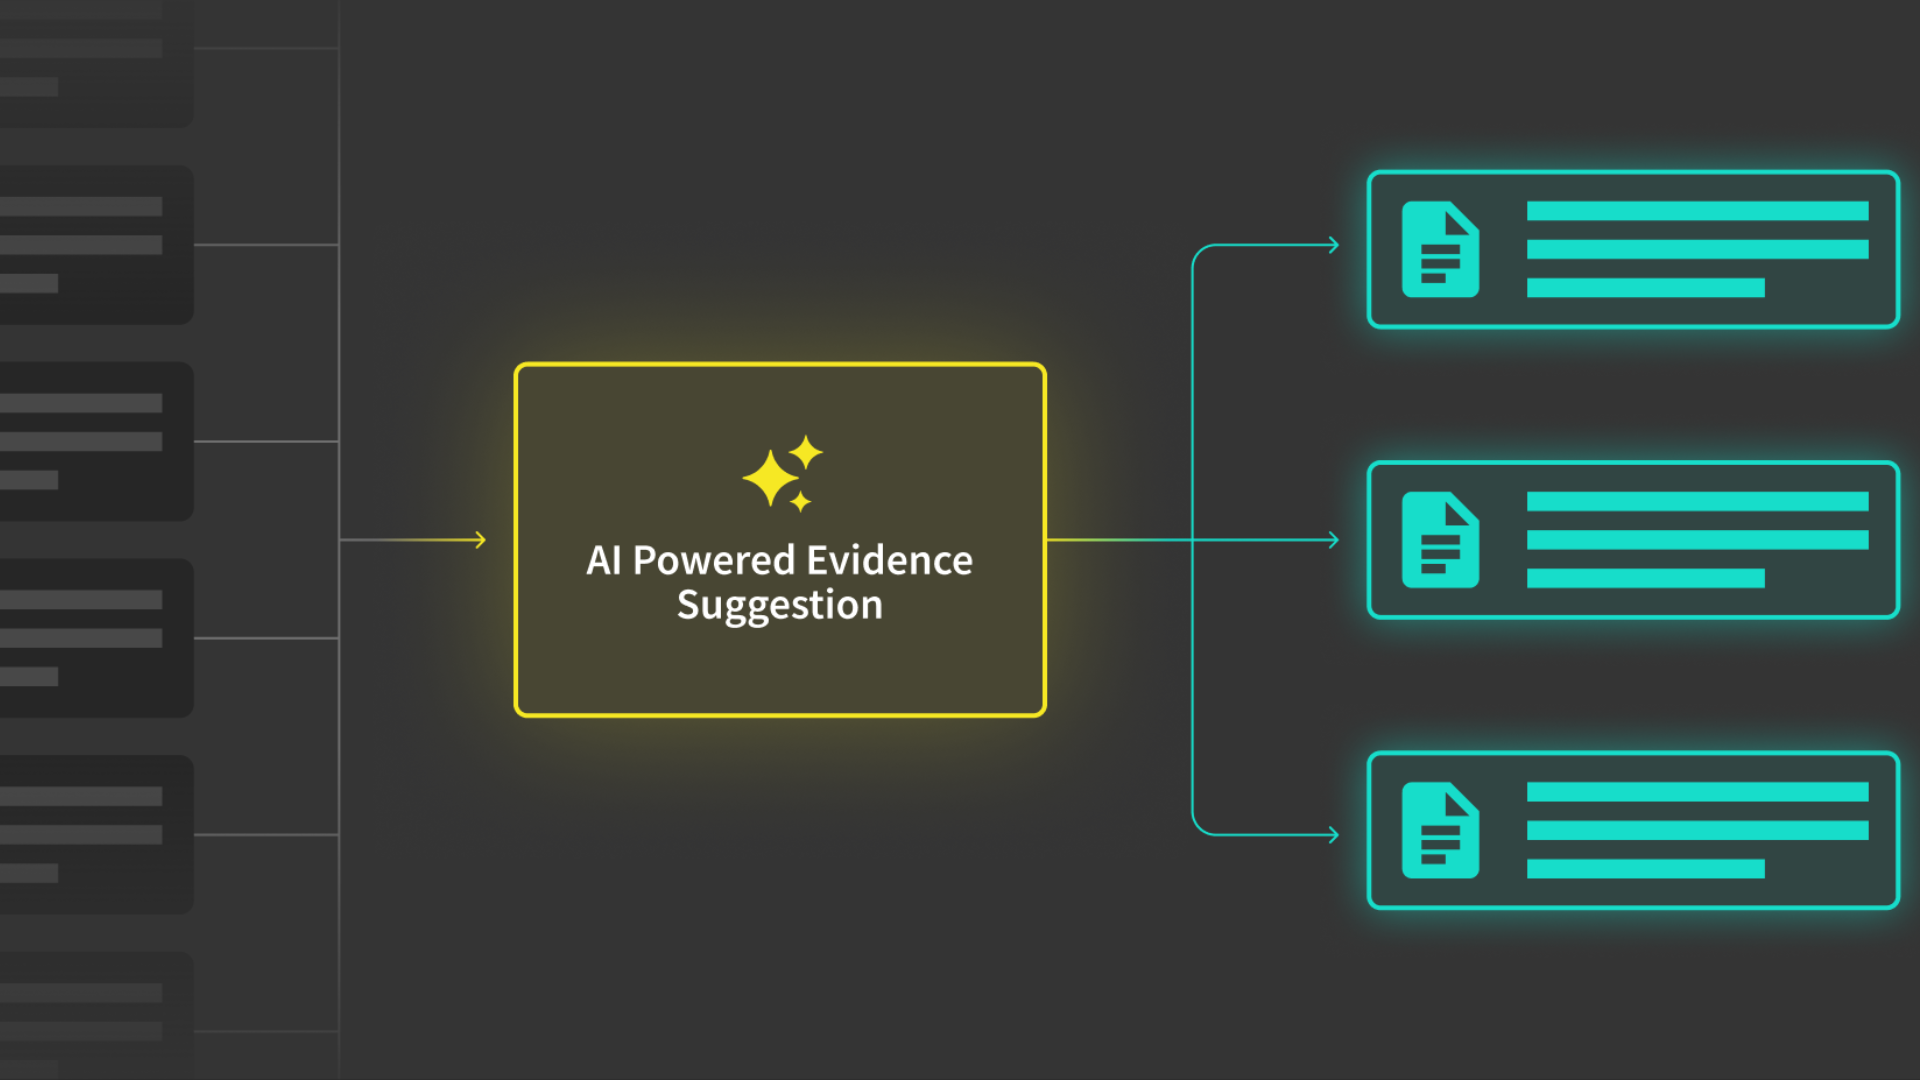
Cloud security platforms are purpose-built to identify what's happening within the cloud environment. A compliance platform should put those findings into the context of the wider programme.
And cloud findings are only one source of that information.
Other signals come from policies, documents, tickets, certifications, risk assessments, evidence and people across the business.
Bringing those different sources together gives organisations a clearer view of how controls are operating, where gaps exist and where action is required.
Bringing cloud security into the wider compliance picture
That's the role Cloud Control Monitoring plays within Hicomply.
Specialist cloud security tools continue doing what they do best: monitoring infrastructure, identifying configuration issues and providing detailed technical findings. Hicomply brings those findings into the wider ISMS, alongside the rest of the compliance programme.
Teams can see which cloud controls are passing or failing, why an issue has been flagged and where attention is required.
But the value isn't simply creating another view of information that already exists elsewhere.
Cloud findings are structured against relevant controls and mapped across the frameworks an organisation manages. This makes technical findings easier for different stakeholders to understand in a compliance context, while helping teams see when one configuration issue affects multiple requirements rather than treating it as a separate task framework by framework.
It also creates shared visibility.
The people responsible for the wider compliance programme aren't necessarily the same people with direct access to, or technical expertise within, specialist cloud security tooling. Bringing relevant findings into the ISMS means Compliance, IT and leadership can work from the same picture, with clearer visibility of what requires attention, who owns it and how remediation is progressing.
As cloud environments change, teams can also identify configuration drift and understand its impact on compliance posture withoutwaiting for a point-in-time review.
Cloud monitoring therefore becomes one part of a much wider view.
Instead of another isolated security dashboard, teams can understand cloud findings alongside the responsibilities, evidence, controlsand progress that make up the wider compliance programme.
That's an important part of continuous compliance: not simply monitoring one part of the organisation more closely, but having the visibility to understand how all of those parts contribute to your compliance posture.
Compliance requires the whole picture
Cloud security is an increasingly important part of demonstrating assurance. But it is one part.
A strong compliance posture comes from understanding how technical security, governance, risk, people, processes and evidence work together.
For me, that's what continuous compliance should ultimately enable.
Not simply more monitoring or more data, but a connected view of the controls, risks, evidence and responsibilities that determine your posture at any given point in time.
Because knowing what's happening in your cloud environment is important.
Understanding how that contributes to the assurance ofyour whole organisation is the bigger picture.